Researcher Analyzes 3,000 Live ClickFix Payloads, Exposing API-Driven Malware Delivery
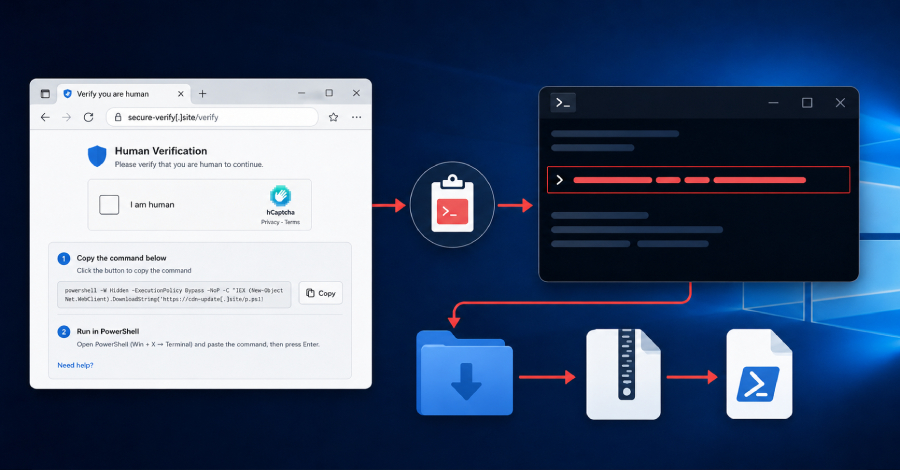
ClickFix, the trick that fools people into running malware by hand, has quietly grown a back office. New research shows the malicious commands behind its fake "prove you're human" pages are now handed out by API-driven servers that give each visitor the same malware in a different disguise. The same research also turne